Company & Industry
News
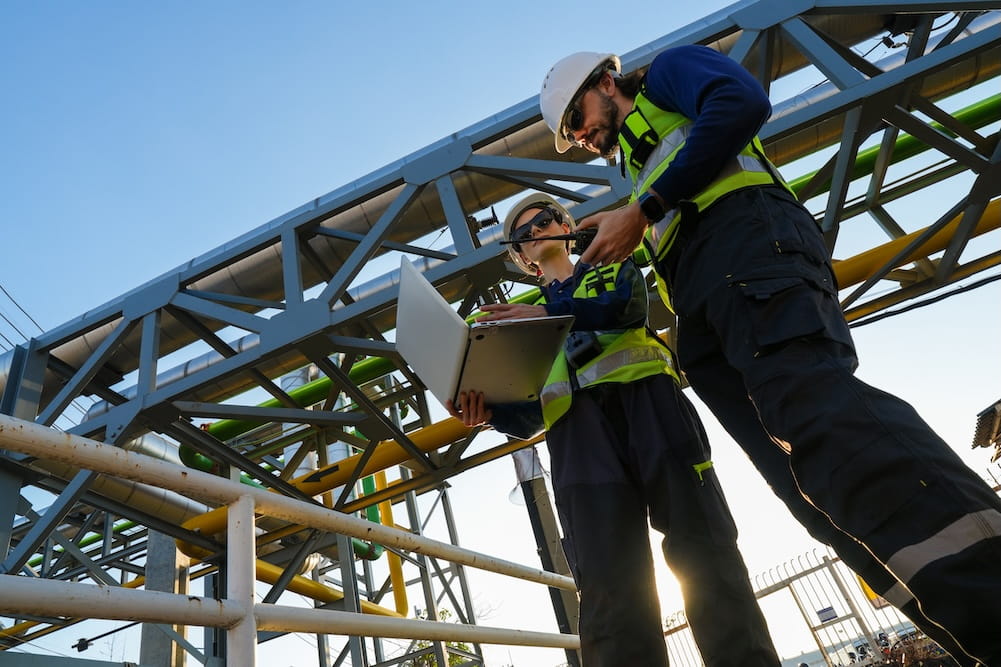
Considerations for Critical Infrastructure Operators Working With Third-Party ICS Integrators
Under NERC CIP-013, entities must work with suppliers, contractors, and OEMs to establish and enforce cybersecurity and supply chain risk management requirements for the procurement and handling of BES Cyber Systems and their associated EACMS and PACS. These...
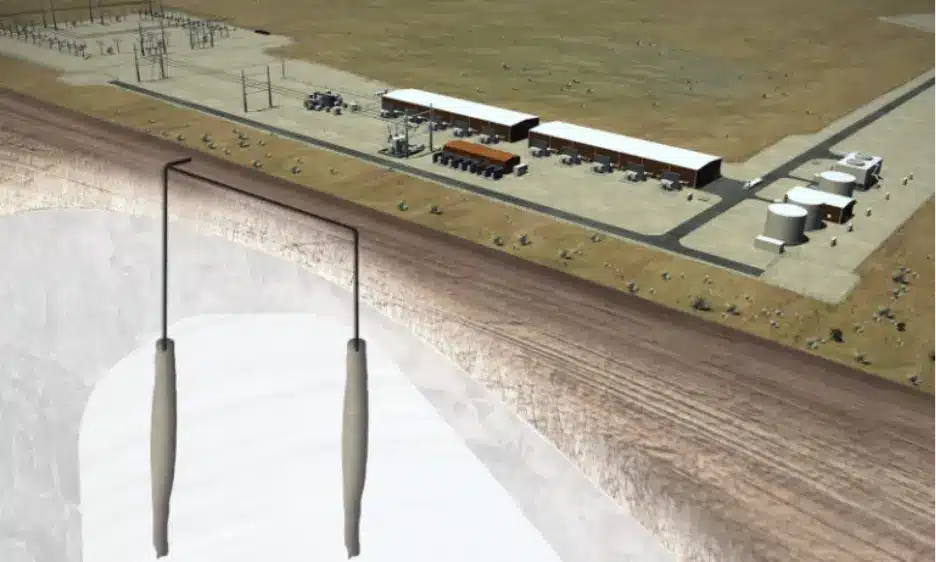
Taking Charge: NAES Tapped to Help Operate First Fully Integrated End-to-End Green Hydrogen Hub
As the energy industry’s leading independent O&M service provider for more than 40 years, NAES is once again on the front lines of innovation. The company assumed care, custody, and control of the ACES Delta hydrogen project in Delta, Utah. This first-of-its-kind facility moves green hydrogen from concept to large-scale…
Powering Mexico Through People, Safety, and Excellence
How a culture of collaboration, accountability, and safety is driving operational excellence across NAES Mexico. By: Lydia Sauer, Communications Associate Reliable power doesn’t happen by chance. Behind every megawatt is a team of professionals committed to operating safely, working collaboratively, and continuously improving the way they serve customers and communities.…
Impulsando a México mediante el talento, la seguridad y la excelencia operacional
La colaboración, la responsabilidad y la seguridad son la base de una cultura que impulsa resultados excepcionales en NAES México. By: Lydia Sauer, Communications Associate Generar energía confiable no ocurre por casualidad. Detrás de cada megavatio hay un equipo de profesionales comprometidos con operar de manera segura, trabajar en colaboración…
CISA’s AI Guidance to Power Plants
By Leonard Wills, NERC Reliability Specialist The power industry continues to deploy AI technologies to analyze operational data, identify equipment anomalies, improve predictive maintenance, and help operators make faster decisions. These capabilities offer operational benefits, but they also introduce AI-related risks that can adversely impact operational technology (OT) environments. CISA’s…

NAES Acquires Industrial Machinery Diagnostics (iMD) Turbine Vibration Subject Matter Experts
ISSAQUAH, Washington (May 4, 2026) - NAES Corporation (“NAES”) announced it has agreed to bring aboard turbine vibration matter experts from Industrial Machinery Diagnostics (iMD) LLC, a premier provider of vibration diagnostics and fault-finding services for rotating equipment. The transaction expands the capabilities of NAES Engineered Performance (EP), strengthening its position as a technical leader in vibration diagnostics and rotating equipment reliability. …

The Grit Behind the Grid: How NAES Sites Defied a Historic Winter
By: Emily Adelman, Corporate Communications Specialist When the forecast turns towards extreme cold and record-breaking snowfall, NAES teams across the country shift into a high-gear culture of preparedness. From the Arctic blasts of New England to the single-digit temperatures of the Texas Panhandle, the NAES approach is defined by Safety and People-First, two of…
EPCm Project Delivery: A Critical Solution for The Thermal Power Build-out in The AI Era
As the world races to expand firm, dispatchable thermal generation to meet the extraordinary electricity requirements of AI and data-center infrastructure, the Engineering, Procurement, and Construction Management (EPCm) model has become an attractive and necessary alternative to conventional EPC contracting. EPCm provides owners & developers with control over procurement, competitive…

Data Center Construction Management
BREAKING THROUGH 2026’S POWER INFRASTRUCTURE BOTTLENECKS A View on 2026’s Power Challenges Data center developers are racing to support AI-driven growth, but a number of challenges persist. Grid constraints, long lead times for critical equipment, and a limited supply of large gas turbines are pushing many to explore unconventional solutions.…
Grid Reliability: What It Really Takes to Keep Power Moving
Keeping the grid stable isn’t just a technical goal — it’s what prevents small problems from turning into major outages. For power generators and utilities, reliability is the day-to-day discipline of keeping critical equipment online, operating within limits, and responding quickly when conditions change. Grid reliability protects more than uptime. It supports economic stability, public…

Beyond Roofs: The Future of Infrastructure Inspection
The Current State of Infrastructure Inspection Most facilities rely on traditional rooftop inspections: technicians walk the roof, capture photos, and compile them into analog or digital reports. These methods are reactive, based on limited surface visuals, and lack spatial precision. Many facility managers shrug at questions like, “What’s the condition of your roof?” because…

How We Make Roof Inspections Safer and Faster
A Smarter, Safer Way to Inspect Roofs For decades, owners of commercial facilities have relied on manual roof inspections, visually scanning surfaces for obvious issues like cracks or leaks, a process that’s time-consuming, subjective, and limited in detecting hidden problems. Advanced technologies like thermal imaging, 3D modeling, high-resolution imaging, and…

Empowering Workers with AI Decision Support in Energy
Artificial intelligence (AI) is often portrayed as a replacement for human work. In reality, when designed thoughtfully, AI serves a very different role in the energy sector: it empowers people to work smarter, faster, and with greater confidence. For power plants and energy operators, AI decision support tools are not…

Predictive Maintenance Gets an Upgrade with Robotics
Predictive maintenance has always been a cornerstone of efficient energy operations. By anticipating equipment failures before they occur, plants can avoid costly downtime, improve safety, and extend asset life. But until recently, predictive maintenance relied heavily on manual inspections and limited data collection. Today, robotics is changing that equation. The…

Solar & Wind Sites 20–74 MW Risk Non-Compliance Due to New Registration Requirements
Issaquah, WA — October 21, 2025 — Hundreds of solar & wind projects once considered outside federal oversight will be required to register and comply with reliability standards for the first time. This closes the long-standing gap that allowed many 20–74 MVA solar & wind plants to avoid registration under the…

Registration is now OPEN for the Compliance Services Conference!
We are excited to invite you to our first-ever Compliance Services Conference taking place this November! This event brings together both NERC and Environmental Compliance professionals for a unified, collaborative experience. It replaces our previous separate conferences and is designed to provide a comprehensive view of compliance across our operations.…

Long-Term Energy Emergency?
By Leland McMillan, NERC Supervisor The Department of Energy has raised concerns with resource adequacy in PJM and is terming it as a possible multi-year Energy Emergency. The recent DOE order states “The emergency conditions resulting from increasing demand and accelerated retirements of generation facilities supporting the issuance of [an…

Data Recovery Strategy for Power Plants
By Leonard Wills, NERC CIP Reliability Specialist A strong data recovery strategy remains critical for business continuity in power plants because any downtime can compromise both operations and compliance. To build an effective strategy, entities must define and align the following: the recovery point objective (RPO), the recovery time objective…

PRC-028 Implementation & Requesting an Extension from Compliance Dates
By Kristina Hannum, Senior NERC Reliability Specialist Understanding PRC-028 & the Unique Challenges for Generator Owners The NERC Reliability Standard PRC-028-1, titled “Disturbance Monitoring and Reporting Requirements for Inverter-Based Resources,” directly impacts Generator Owners (GO) with solar, wind, battery storage, and other inverter-connected generation facilities. This standard mandates comprehensive data…

Powering the Future: Why Grid Modernization Is No Longer Optional
By Joshua Brantley, Senior NERC Reliability Specialist The electrical industry is undergoing one of the most significant transformations in its history. For decades, the power grid has been the backbone of industrial growth, economic development, and everyday life. Yet much of this infrastructure was built in the mid-20th century, designed…

New naming conventions for NERC registration and Category 2 Registration requirements
By Laura Christensen, Senior NERC Reliability Specialist The North American Reliability Corporation (NERC) has introduced new terminology – Category 1 and Category 2 – to distinguish between different groups of inverter-based resources (IBRs) in its expanded Generator Owner (GO) and Generator Operator (GOP) registration regime. All currently registered NERC entities…