By Leonard Wills, NERC CIP Reliability Specialist
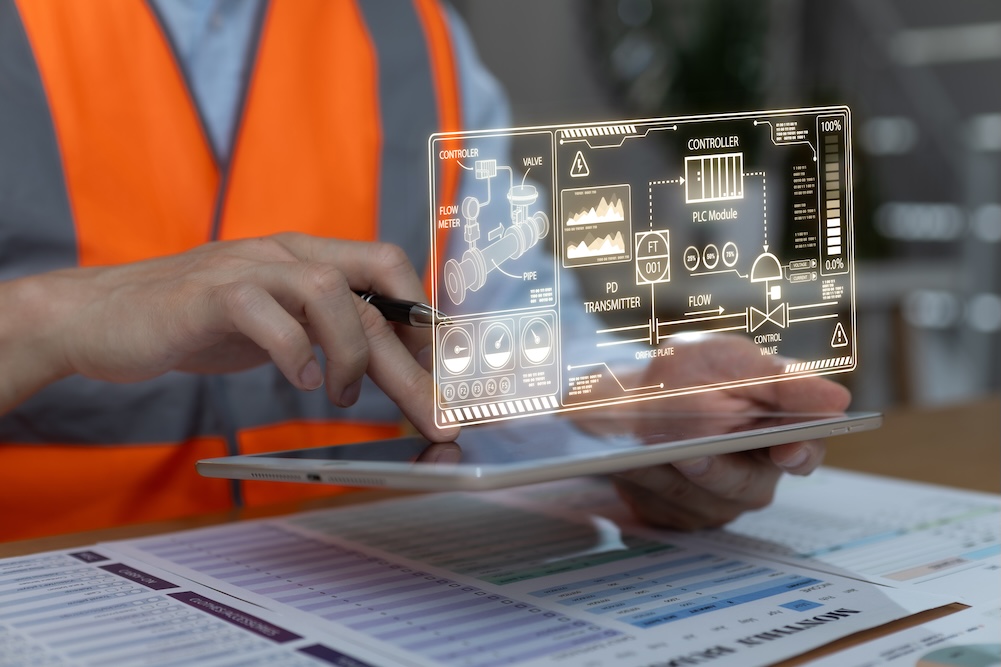
For years the comfort in generation was that attacking a PLC took rare skill. You had to understand S7 comm or Modbus, the memory map, the engineering tooling, and how a specific controller behaved when you poked it. That barrier is gone. On August 19, 2026, NSA, CISA, FBI, DOE, and EPA released joint advisory AA26-231A warning that threat actors are actively targeting Siemens S7 Series PLCs that are exposed to the internet or insufficiently segmented from it. The new element is the tooling: the scripts are AI-generated Python built on the open-source python-snap7 library, disguised as legitimate OT monitoring tools, and they grant read/write access to PLC memory and ladder logic. The advisory spans the entire S7 line, from the S7-200 through S7-1500 F-series safety controllers, and names Energy among the most exposed sectors.
This is the first government advisory to explicitly attribute an active OT attack campaign to AI-generated tooling, and it follows AA26-097A from April 2026, which documented Iranian-affiliated actors targeting water utilities across 12 states. The targeting is not exotic. Attackers use Censys and ZoomEye to scan for internet-exposed Siemens S7 devices, and the vulnerability lies in internet exposure and known misconfigurations rather than zero-days. The advisory is also clear that PLC targeting is broader than Siemens and that all PLC owners, regardless of vendor, should apply the mitigations.
Why this lands on generation: walk any plant and count the PLCs that are not the DCS. Water treatment, fuel handling, ash and emissions systems, HVAC for the control building, turbine auxiliaries, the OEM skid that came with its own controller and cellular modem. Many of those are not BES Cyber Systems or sit in a low-impact classification where nobody has run a baseline. A script that looks like monitoring traffic will not trip a signature, and a PLC with no logging will not tell you it was read.
What to do this month. Inventory every S7 device on the network, which is also the advisory’s first recommendation, and then do the same for every other PLC brand on site. Confirm none of them is reachable from the internet, including through a vendor modem you forgot about. Apply available Siemens patches, and where you cannot patch, put the controller behind something that can be. The advisory emphasizes foundational controls, not AI-based defenses, and that is the point: the attacker’s barrier got cheaper, so your basics must be real.